WEBINAR
Share:

Vendor Assurance for AI and Cloud-Based GxP Systems

What You Can Leverage, Challenge, and Independently Verify

  • Date
    28 October 2026
  • 11.00 AM Eastern Time (US/Canada)
    03.00 PM GMT

Course is now LIVE. Click below to join the session.

The webinar provides a practical framework for assessing vendor assurance without unnecessarily duplicating vendor activities. It also addresses common gaps such as unclear shared responsibilities, insufficient transparency of AI models and changes, weak data-governance controls, and over-reliance on certifications. The result is a more efficient, defensible, and inspection-ready approach to supplier and system assurance.

/* Hide default + / - icon */ .accordion-toggle-icon { opacity: 0; } /* Add circle instead */ .accordion-header::after { content: "○"; font-size: 18px; margin-left: auto; transition: 0.2s ease; } /* When open → filled circle */ .accordion-item.active .accordion-header::after { content: "●"; } /* Hide default + / - icon */ .accordion-toggle-icon { opacity: 0; } /* Add circle instead */ .accordion-header::after { content: "○"; font-size: 18px; margin-left: auto; transition: 0.2s ease; } /* When open → filled circle */ .accordion-item.active .accordion-header::after { content: "●"; } .accordion-header::after { content: "◯"; font-size: 18px; transition: transform 0.25s ease; } .accordion-item.active .accordion-header::after { transform: rotate(90deg); }
REGISTRATION OPTIONS

Live session Plus
Complimentary 30 Days Streaming access

$290  |  One participant (viewer)

$390  |  Team (2 - 5 participants)

$490 |  Team (6 - 10 participants)

REGISTER FOR THE COURSE

US $290 per learner

30-Days Unlimited Streaming Access

/* Hide default + / - icon */ .accordion-toggle-icon { opacity: 0; } /* Add circle instead */ .accordion-header::after { content: "○"; font-size: 18px; margin-left: auto; transition: 0.2s ease; } /* When open → filled circle */ .accordion-item.active .accordion-header::after { content: "●"; } /* Hide default + / - icon */ .accordion-toggle-icon { opacity: 0; } /* Add circle instead */ .accordion-header::after { content: "○"; font-size: 18px; margin-left: auto; transition: 0.2s ease; } /* When open → filled circle */ .accordion-item.active .accordion-header::after { content: "●"; } .accordion-header::after { content: "◯"; font-size: 18px; transition: transform 0.25s ease; } .accordion-item.active .accordion-header::after { transform: rotate(90deg); }

REGISTER FOR THE COURSE

To Get 30-Day Access to ONLY this Course 

US $290 per learner
  • This course is Included in Subscription Pack
Subscription include access to entire Learning Library
/* Hide default + / - icon */ .accordion-toggle-icon { opacity: 0; } /* Add circle instead */ .accordion-header::after { content: "○"; font-size: 18px; margin-left: auto; transition: 0.2s ease; } /* When open → filled circle */ .accordion-item.active .accordion-header::after { content: "●"; } /* Hide default + / - icon */ .accordion-toggle-icon { opacity: 0; } /* Add circle instead */ .accordion-header::after { content: "○"; font-size: 18px; margin-left: auto; transition: 0.2s ease; } /* When open → filled circle */ .accordion-item.active .accordion-header::after { content: "●"; } .accordion-header::after { content: "◯"; font-size: 18px; transition: transform 0.25s ease; } .accordion-item.active .accordion-header::after { transform: rotate(90deg); }
  • Faculty
    Milan Kučera
  • Duration
    90 Minutes
  • Course ID
    TF1331
  • Live Q&A +
    Post-live Continued Learning
  • Presentation Handout
    & Templates
  • Assessment
    & Certification Included


Why take this course?

AI-enabled and cloud-based GxP systems increasingly depend on vendors for infrastructure, software development, security, data management, AI models, monitoring, and ongoing change. This creates a practical validation question: which vendor evidence can be leveraged, which claims must be challenged, and which controls or outcomes must be independently verified by the regulated company?

This webinar presents a risk-based approach to vendor assurance that goes beyond collecting certificates and supplier questionnaires. It addresses how to evaluate vendor documentation, audit evidence, validation packages, cloud controls, AI lifecycle information, data governance, service-level commitments, and change-management practices. Particular attention is given to defining the regulated company’s responsibilities under shared-responsibility models and to maintaining sufficient control over GxP-relevant data and decisions.

The traditional supplier-qualification approach is often not sufficient for modern cloud and AI-enabled GxP systems. Vendors may provide extensive evidence, but regulated companies remain accountable for determining whether that evidence is relevant, current, complete, and appropriate for the intended use. Participants will learn how to distinguish evidence that can reasonably be leveraged from evidence that requires challenge or independent verification.

Learning Objectives
  • Apply a risk-based framework for vendor assurance of cloud-based and AI-enabled GxP systems.
  • Distinguish vendor evidence that can be leveraged from evidence that should be challenged or independently verified.
  • Evaluate shared-responsibility models and identify retained responsibilities of the regulated organization.
  • Assess vendor controls for data integrity, security, AI lifecycle management, monitoring, and change control.
  • Define proportionate audit, assessment, and verification activities based on GxP impact and system risk.
  • Recognize common vendor-assurance weaknesses that can create inspection and validation risks.

Key Areas Covered

  • Vendor assurance in the context of GxP computerized systems and cloud services
  • Shared responsibility: what the vendor controls versus what the regulated company must control 
  • Vendor documentation: certificates, audit reports, validation packages, testing evidence, and technical documentation
  • AI-specific assurance: model lifecycle, training data, monitoring, drift, transparency, and change management
  • Data integrity and security controls in cloud environments 
  • How to challenge vendor claims and identify evidence gaps 
  • Independent verification: when it is necessary and how far it should go 
  • Building an inspection-ready vendor assurance package 

Who Must Attend

  • Quality Assurance Departments
  • Regulatory Affairs Departments
  • IT and Digital Transformation Departments
  • Manufacturing and Operations Departments
  • CSV and CSA Specialists
  • System Owners and Subject Matter Experts
  • Data Integrity Specialists
  • AI Governance Teams
  • Compliance and Audit Managers
  • SaaS and Cloud Service Providers
  • Vendors and Consultants Supporting GxP Systems
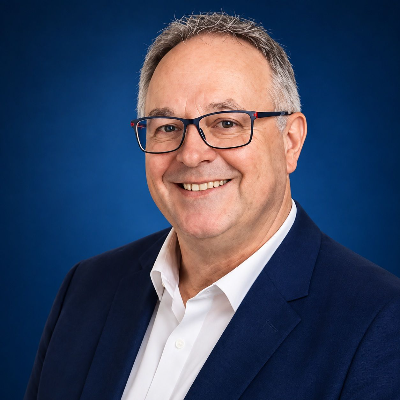
Milan Kučera
COURSE DIRECTOR

Milan Kučera

Milan Kučera is a senior validation and GxP technology professional focused on computerized systems, laboratory systems, data integrity, cloud environments, and emerging technologies in regulated organizations. His work combines practical validation and compliance expertise with a strong focus on risk-based approaches, quality strategy, and inspection readiness. He has a particular interest in the application of modern technologies, including cloud computing and AI, within regulated GxP environments, with emphasis on governance, data integrity, validation strategy, lifecycle management, and effective human oversight. His approach is to translate complex regulatory and technological expectations into practical controls, evidence, and implementation strategies that can be applied by Quality, IT, validation, and business teams.

If you would like to request a Proforma invoice to sign up for this course. please click here

Commonly Asked Questions About This Subject

The following questions address practical regulatory, compliance, validation, quality, operational, and inspection-related considerations commonly associated with this subject.

How should a regulated company respond when a critical vendor refuses to provide detailed evidence because of confidentiality or security restrictions? 

A refusal to provide underlying evidence does not automatically make the vendor unacceptable, but it changes what can reasonably be relied upon. The regulated company still needs enough evidence to understand whether controls supporting its GxP use are operating effectively. 


This situation is common with large cloud and AI providers. Detailed architecture, penetration testing, source code, training data, model information, or internal validation records may be restricted. Repeatedly requesting information the vendor will never release adds little value. 


The assessment should instead identify the assurance question that remains unanswered. Independent audit reports, controlled demonstrations, summarized test evidence, contractual commitments, performance records, third-party assessments, or targeted customer verification may provide sufficient evidence for some risks. 


Inspection exposure develops when the qualification record simply states that information was "vendor confidential" and closes the issue. Restricted access explains why evidence was unavailable. It does not explain why the remaining evidence was sufficient to support continued reliance on the service. 

What should happen when a vendor has strong certifications and audit reports but recurring problems continue to affect the regulated company's GxP use? 

Operational performance should cause the original vendor assurance conclusion to be reassessed. Certifications and successful audits provide useful evidence about the vendor's control environment, but recurring incidents can show that those controls are not adequately protecting the customer's specific regulated use. 


Consider repeated interface failures, unexpected configuration changes, delayed incident notifications, data availability problems, or defects introduced through releases. None necessarily invalidates a vendor's certification. They do, however, change the evidence available to the regulated company. 


This is where supplier files can become disconnected from operational experience. The vendor remains classified as acceptable because the scheduled reassessment is current while system owners repeatedly manage problems outside the qualification process. 


A stronger governance model feeds significant incidents, service performance, deviations, change history, and unresolved issues back into vendor assurance. Continued reliance should reflect current evidence rather than the strength of the vendor's original qualification package. A certificate cannot outweigh persistent evidence from the service actually being used. 

How can a company defend relying on vendor testing when it has never independently reproduced the vendor's tests? 

Reproducing vendor testing is unnecessary when the company can demonstrate why that evidence is credible, relevant to its intended use, and applicable to the configuration being relied upon. Independent verification should address remaining uncertainty rather than mechanically repeat work already performed competently. 


The difficult judgment concerns applicability. A vendor may provide extensive functional and regression testing for the standard platform, while the regulated implementation depends on customer-specific configurations, workflows, permissions, interfaces, calculations, or AI-assisted functions. Vendor evidence may strongly support the base product while providing little assurance for those implementation-specific elements. 


The assessment should therefore show which assurance questions the vendor evidence answers and which remain with the regulated company. Supplier capability, test scope, configuration, traceability, results, deviations, and change controls all affect how much reliance is reasonable. 


Inspection defensibility comes from showing why evidence was accepted. "Vendor tested" is a conclusion. The supporting record should demonstrate why that testing was sufficient for the particular GxP function under review. 

What creates the greatest vendor-assurance risk after an AI or cloud system has been successfully qualified and used for several years? 

The original qualification can gradually stop describing the service that is actually being used. Cloud platforms, underlying infrastructure, security controls, integrations, subcontractors, AI models, data practices, and service capabilities can change substantially while the vendor itself remains approved. 


This becomes difficult to detect when periodic reassessment concentrates on renewed certificates, questionnaires, and contracts. Those records may remain current while the technical basis for the original assurance decision has materially changed. 


A mature review should ask what has changed since the previous assessment and whether those changes alter assumptions the regulated company relies upon. Significant incidents, vendor acquisitions, new subprocessors, major platform migrations, AI model changes, altered data handling, service changes, and recurring performance issues can all justify deeper review. 


Historical qualification provides useful evidence of where the relationship began. Continued vendor assurance depends on knowing whether the conditions supporting that original decision still exist. 

Your TalkFDA Webinar Experience

When you reserve your seat, everything is organized for you — from access to certification from one place.

1. Confirmation

You receive a confirmation email and your course appears instantly in your TalkFDA dashboard.

2. Your Course Hub
Your TalkFDA course page becomes your central hub where you can join the session, access materials, and manage your learning.

3. Join the Live Training
At the scheduled time, click Join Session and you’ll be connected to the live Webex session with the instructor.

4. Watch Again Anytime
After the session, the playback becomes available on the same course page so you can revisit important sections.
5. Earn Your Certificate
Complete the course and your certificate is unlocked automatically in your learning history.

Everything related to your webinar: access, materials, playback, and certification — lives in one place.
Simple. Organized. Professional.
Go ahead and reserve your seat with confidence.

Built on 20+ years of global regulatory training experience across FDA, EMA, MHRA, and ICH frameworks.
Trusted by professionals across 80+ countries.

Testimonials

This is an upcoming session. Feedback below reflects experiences from similar programs delivered by our expert faculty.

“Session was easy to follow even for non-core team members. That helped.”
- Production Officer
“Good balance. Not too basic, not too deep. Worked well for mixed team.”
- Manager, Regulatory Affairs
“Team found it useful. Especially for aligning understanding across functions.”
- Director, Operations

Ready to Strengthen Your Team? Let’s Build Your Training Plan.

Whether you’re looking for a single onsite workshop or a multi-team training series, we’ll help you design a program that fits your goals, timelines, and operational reality.

Your team deserves the clarity.
Your organization deserves the confidence.

Upcoming Courses

Featured Courses