Why take this course?
Software validation observations continue to appear in FDA warning letters, inspection observations, and consent decrees across regulated industries. Recurring weaknesses involve validation scope, risk assessment, user requirements, testing rationale, change management, electronic records, data integrity controls, and ongoing system oversight. These findings can affect systems already supporting manufacturing, quality, laboratory, clinical, or business operations, where continued reliance depends on adequate validation evidence and controls.
This webinar examines recurring software validation patterns through regulatory enforcement actions and remediation efforts. Participants will consider how validation decisions create long-term compliance exposure, how weaknesses are identified during inspections, and what evidence inspectors expect when those decisions are challenged. The discussion also addresses 21 CFR Part 11, 21 CFR Parts 210 and 211, risk-based validation, change management, and FDA remediation expectations following significant findings, with emphasis on strengthening validation programs before similar deficiencies attract regulatory attention.
Key Areas Covered
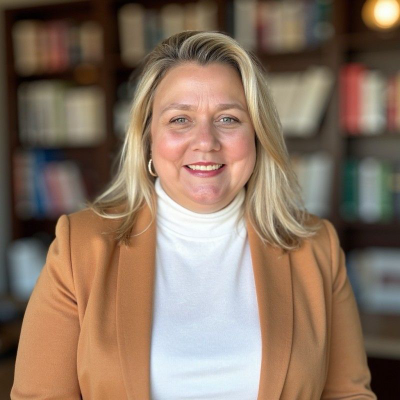
Meredith Crabtree
Meredith Crabtree has over 30 years of experience across regulated industries, including pharmaceutical, medical device, laboratory, blood, plasma, tissue, cosmetics, supplements, and animal health operations. Her consulting work includes regulatory assessments, third-party inspections, Consent Decree support, recall support, and Quality training, directly supporting the enforcement, remediation, and compliance issues addressed in this webinar.
Commonly Asked Questions About This Subject
Why can a software validation package that looked acceptable at implementation become difficult to defend several years later?
The original validation may still be technically sound, but the evidence can lose relevance as the operating system changes around it. FDA enforcement examples repeatedly involve systems already supporting routine regulated operations where validation, change management, risk controls, or continuing oversight were considered insufficient.
The weak point is often cumulative change. Configuration changes, new interfaces, revised workflows, infrastructure updates, patches, additional users, altered data flows, and procedural workarounds can gradually create a production environment that no longer matches the assumptions behind the original validation.
This becomes visible during inspection when an investigator selects a current function or electronic record and asks how its validated state is supported. A historical protocol and approval report provide limited assurance if nobody can connect them convincingly to today's configuration and use.
Periodic review carries more weight when it examines whether previous validation conclusions remain applicable, rather than simply confirming that required validation documents still exist.
What should a company do when it discovers during an inspection that a routinely used GxP function was never included in the original validation scope?
The first decision should address current product, process, and data risk rather than rushing to generate missing validation documentation. The company needs to establish how the function has been used, what regulated decisions or records depended on it, and whether existing evidence provides any support for continued reliance.
Retrospective paperwork becomes problematic when it attempts to recreate evidence that should have existed before operational use. A newly written requirement or protocol cannot demonstrate what was known, assessed, or tested years earlier.
The investigation should reconstruct the function's history using available configuration records, change controls, incidents, user records, system evidence, and operational data. Current testing may establish present performance, but it should be clearly distinguished from evidence of historical control.
This distinction matters because FDA enforcement concerns can extend beyond missing documentation to weaknesses in validation scope, risk assessment, and the basis for relying on regulated software. A credible remediation record acknowledges the gap and evaluates its consequences.
How far should remediation extend when an FDA observation identifies a validation weakness in only one computerized system?
A significant finding should trigger an assessment of whether the same decision-making weakness exists elsewhere. Correcting only the cited system can leave the underlying validation problem untouched when the cause lies in procedures, risk methodology, governance, change management, or validation practices used across multiple systems.
Suppose an investigator finds that one system's testing did not adequately address a critical electronic-record function. If the same validation procedure, risk-assessment method, template, or approval practice was used for twenty other systems, those systems become relevant to the remediation decision even without individual observations.
This is where remediation scope can become difficult to defend. A narrow CAPA may correct the visible deficiency while failing to examine whether the same conditions produced similar gaps elsewhere.
FDA enforcement patterns described for software validation include broader weaknesses in validation decisions and system oversight, rather than only isolated missing documents. A defensible remediation therefore explains how systemic extent was evaluated and why additional systems were included or excluded.
What weakens a remediation program when large numbers of legacy systems require validation correction at the same time?
Treating remediation as a document-production exercise can create impressive completion numbers without resolving the weaknesses that caused the regulatory concern. Under pressure, teams may prioritize protocols, traceability matrices, risk assessments, and summary reports because those deliverables are easy to count.
The more important question is whether the remediation has produced reliable evidence for the system currently supporting GxP operations. That may require resolving undocumented configurations, evaluating historical changes, challenging inherited requirements, investigating unexplained discrepancies, and determining whether existing testing remains applicable.
Risk-based prioritization also needs technical substance. Labeling systems "high," "medium," or "low" risk provides little protection if the classification does not influence remediation depth, sequencing, interim controls, or testing.
FDA enforcement concerns around software validation can involve validation scope, risk assessment, change management, electronic records, data integrity, and continuing oversight. Closing remediation actions quickly is less persuasive when the evidence still cannot explain why continued reliance on the affected systems is justified.
Your TalkFDA Webinar Experience
1. Confirmation
3. Join the Live Training
4. Watch Again Anytime
Testimonials
Ready to Strengthen Your Team? Let’s Build Your Training Plan.
Your team deserves the clarity.
Your organization deserves the confidence.
Upcoming Courses
Featured Courses